Forum hacked?

Status
Not open for further replies.

r32

New member
FYI guys

Looks like it got hacked. Would definitely avoid downloading anything from this site, just to be safe. Probably change your password too if you can. Or just don't login right now. No forced https? Be careful since it looks compromised.

Software used for this forum is vBadvanced CMPS v3.2.2
Current Version: 4.3.0 (Released 05-13-2014) (hasn't been maintained in 4+ years. Ouch.)

And vBulletin used for this forum is vBulletin Version 3.8.7 (2009 holy shit man!)
Current Version: 5.4.5 (November 14, 2018)

Forum software is at least 5 years out of date. Holy shiiiiiz. Basically an accident waiting to happen. vBadvanced CMPS v3.2.2 appears to be around 2012 and I'm seeing known exploits with version 3.2.2 google search. Is site owner over his head on keeping forum software upgraded? I hope they have a db backup, otherwise they are really up a creek without a 4Runner.
 
Last edited:
Register to hide this ad
FYI guys

Looks like it got hacked. Would definitely avoid downloading anything from this site, just to be safe. Probably change your password too if you can. Or just don't login right now. Also, site is NOT HTTPS which means no SSL certificate, so be careful here, since it looks compromised. This should be pinned at top of all forums and posting should be turned off until solved.

Software used for this forum is vBadvanced CMPS v3.2.2.
Current Version: 4.3.0 (Released 05-13-2014) (hasn't been maintained in 4+ years. Ouch.)

And vBulletin used for this forum is vBulletin Version 3.8.7
Current Version: 5.4.5 (November 14, 2018)

Forum software is at least 5 years out of date. Holy shiiiiiz. vBadvanced CMPS v3.2.2 appears to be around 2012 and I'm seeing known exploits with version 3.2.2 google search. Is site owner over his head on keeping forum software upgraded? I hope they have a db backup, otherwise they are really up a creek without a 4Runner.

Yeah it's kind of odd that this site has sponsors and such yet they don't bother updating the software behind it.
 
Yep. Shocked the software is so out of date. Absolutely no excuse for that and puts everyone's info in jeopardy. Additionally, no SSL certificate. Really? It costs about $50/year, or even free now if you use the free SSL from the Let's Encrypt project (if money to run site is an issue).
 
Last edited:
I have always thought that there's really no excuse for not having an SSL cert at the very least. Struck me as odd that a forum of this size is lacking one.
 
Google has even lobbied to make SSL certificates mandatory across all websites because they believe all sites should have it.

And there is a group of talented people that got together to provide free SSL certificates for any site, because they too believe, protection is critical and that ALL websites should have an SSL, no matter what. But a big site like this, with 1000's of users without an SSL? Almost unheard of.

https://letsencrypt.org/
 
Google has even lobbied to make SSL certificates mandatory across all websites because they believe all sites should have it.

And there is a group of talented people that got together to provide free SSL certificates for any site, because they too believe, protection is critical and that ALL websites should have an SSL, no matter what. But a huge site like this, with 1000's of users without an SSL? Almost unheard of.

https://letsencrypt.org/

Actually it seems that the forum does use an SSL certificate if you manually enter https at the front of the URL. From experience I know it's not easy to retroactively secure all content across the site though and that's why it shows "Your connection to this site is not fully secure".
 
It is definitely possible, if site is configured correctly and maintained. Of course you're right in that there could be mixed content on the site from embedded images from sites that aren't HTTPS but everything else should be served up https without a doubt. They could only allow embedded images from free site like IMGUR as possible solution?
 
Correct, there is a certificate for the HTTPs connection. Just change your default/bookmark to that

Also, what happened that prompted this discussion. It looked as though it was down for DB maintenance last night
 
Correct, there is a certificate for the HTTPs connection. Just change your default/bookmark to that

Also, what happened that prompted this discussion. It looked as though it was down for DB maintenance last night

Look at cookie crumb links "Toyota 4Runner Foruma" and title of 4th gen forum "4th Gen T4Rssssssssssssssssssss"
 
Looks like it.

As far as information being compromised, I'm not exactly sure what you're worried about. First, the assumption should always be that a site is not secure - and everyone should be able to tell if a site is using https or not. There's a reason all modern browsers now have this information prominently displayed.

The only personal information on this forum is what you registered with. For me, that's my email address and a random password that I use on sites like this. Email addresses really don't matter - your email address is already floating around in millions of places. The password doesn't matter, either. I use it nowhere else.

If you want to stay safe:
-Use a different password everywhere, especially those with sensitive information. Chrome browser now has a strong password generator built-in, which is really quite nice for using a unique password for every site.
-Use the "HTTPS Everywhere" browser extension. Won't work here of course, but no reason to not use it. Forces website, when available, to use https.
 
Look at cookie crumb links "Toyota 4Runner Foruma" and title of 4th gen forum "4th Gen T4Rssssssssssssssssssss"

Yeah big time broken backlinks and addresses, I'm really surprised the site architecture is so pieced together, most SEO/marketing/site-owner guys would clean up all the broken links and addresses just for site function yet alone for Google search criteria. I thought for sure last night/this morning it was hacked.
 
Would this explain why I was getting "database errors" when I tried to visit this site from last night until late this morning?
 
Looks like it.

As far as information being compromised, I'm not exactly sure what you're worried about.

It's just about emails and passwords. Links provided in posts, ad links, etc. can be easily changed to malware links and stuff of that nature. That's something users should be concerned with if the site is compromised. I've seen enough hacked sites over the years to know what kind of comprises can happen.
 
I'm sure they would upgrade if the new software wasn't such a pile of crap or so f'ing expensive. I can't remember the last time I paid to access the site? Can you? Running this board is no picnic and no one is getting rich...


Use a unique user name and for god sakes a totally unique password for each site you visit. That will go a long way to keeping your info safe.

Using the password 'MonkeySex24/7' at every site you visit is not a great security model.
 
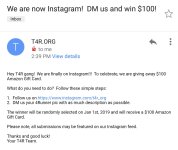
I assume this is the next step in the hacking process? I'm certainly not clicking through.
 

Attachments

  • Screenshot_20181211-145420~2.jpg
    Screenshot_20181211-145420~2.jpg
    106.3 KB · Views: 1,211
Status
Not open for further replies.

Members online

Forum statistics

Threads
278,306
Messages
3,554,045
Members
248,016
Latest member
Advally Service

Trending content

Back
Top