Thai
Elite Member
Link: 10 million Android phones infected by all-powerful auto-rooting apps | Ars Technica
"Accessing these devices and their sensitive data creates a new and steady stream of revenue for cybercriminals," Check Point researchers wrote in a recently published report. "Emboldened by financial and technological independence, their skillsets will advance–putting end users, enterprises, and government agencies at risk."
While profit is powerful motivation for any attacker, Yingmob’s apparent self-sufficiency and organizational structure make it well-positioned to expand into new business ventures, including productizing the access to the 85 million Android devices it controls. This alone would attract a whole new audience–and a new stream of revenue–for Yingmob. Quick, easy access to sensitive data on mobile devices connected to enterprises and government agencies around the globe is extremely attractive to cybercriminals and hacktivists.
Under a model known as sandboxing, most Android apps aren't permitted to access passwords or other data available to most other apps. System applications with root, by contrast, have super-user permissions that allow them to break out of such sandboxes. From there, root-level apps can read or modify data and resources that would be off-limits to normal apps.
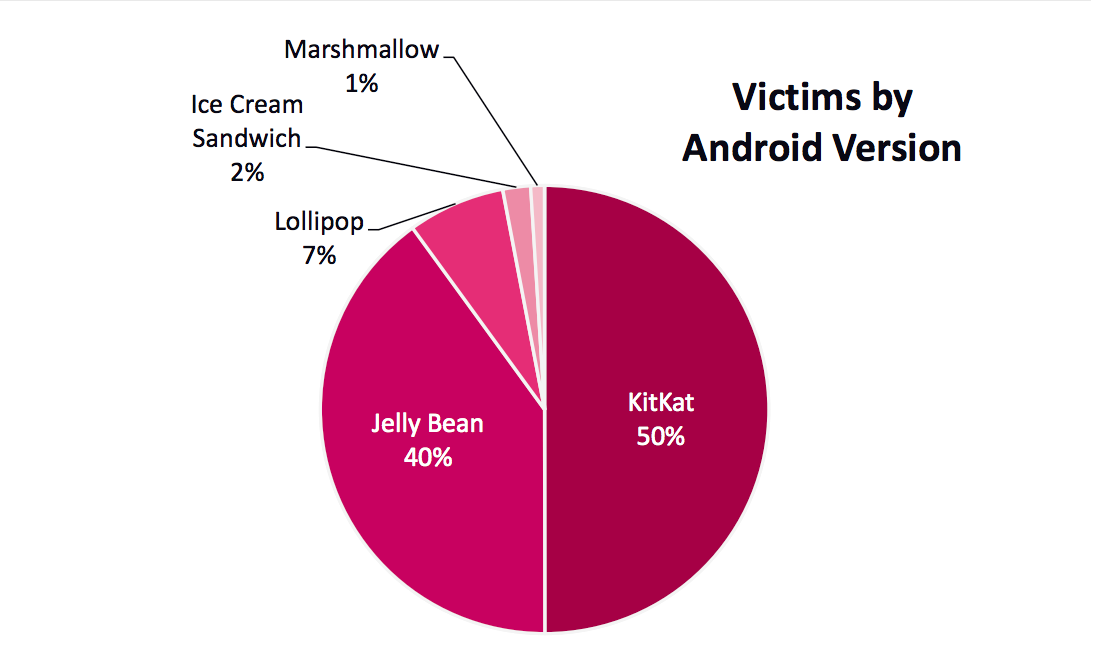
Still, US-based infected phones total almost 287,000. The most widely infected major Android versions are KitKat with 50 percent, followed by Jelly Bean with 40 percent. Lollipop has 7 percent, Ice Cream Sandwich has 2 percent, and Marshmallow has 1 percent.
"Accessing these devices and their sensitive data creates a new and steady stream of revenue for cybercriminals," Check Point researchers wrote in a recently published report. "Emboldened by financial and technological independence, their skillsets will advance–putting end users, enterprises, and government agencies at risk."
While profit is powerful motivation for any attacker, Yingmob’s apparent self-sufficiency and organizational structure make it well-positioned to expand into new business ventures, including productizing the access to the 85 million Android devices it controls. This alone would attract a whole new audience–and a new stream of revenue–for Yingmob. Quick, easy access to sensitive data on mobile devices connected to enterprises and government agencies around the globe is extremely attractive to cybercriminals and hacktivists.
Under a model known as sandboxing, most Android apps aren't permitted to access passwords or other data available to most other apps. System applications with root, by contrast, have super-user permissions that allow them to break out of such sandboxes. From there, root-level apps can read or modify data and resources that would be off-limits to normal apps.
Still, US-based infected phones total almost 287,000. The most widely infected major Android versions are KitKat with 50 percent, followed by Jelly Bean with 40 percent. Lollipop has 7 percent, Ice Cream Sandwich has 2 percent, and Marshmallow has 1 percent.